

Is your system safe, and what would it take to fix it?
The Architecture and Security Review is two weeks in which the engineers who would fix your system review it against OWASP and good practice. You get written findings ranked by risk, each with a plain explanation and an effort estimate, and a 90-day plan.
- Two weeks
- Up to 8 at the closing session
- On site or remote
Fix these first.
Who is this for?
CTOs, IT leads and owners with a system nobody fully trusts.
Does any of this sound familiar?
- A previous vendor built it and walked away.
- The one person who understood it has left.
- It was built in a hurry for a launch, and nobody has looked under the hood since.
Not the right fit if
-
You need a penetration test
-
You need a certificate for a client or a regulator
What happens in the room?
Two weeks, plus a 90-minute closing session.
- Part 1
Most of the work happens before anyone meets. In the first days we hold a short call with whoever runs your infrastructure, agree which scans run and when, and get read-only access. A senior engineer then reads your code, configuration and hosting setup across five areas: architecture, code, security, infrastructure and operations.
- Part 2
In the first week we also interview the people who run the system: who can deploy, how incidents are handled, and what nobody wrote down. Halfway through, we send a short check-in on what we have found so far. If we find anything critical, such as a live password in a repository, we tell you that day. We do not wait for the report.
- Part 3
The two weeks end with a 90-minute closing session, remote or on-site. We walk you through every critical and high finding, agree the order of fixes with you, and hand over the report.
What do you leave with?
You leave the closing session with the review report. It starts with a map of how your system fits together. Then come the findings, ranked from critical to low, each with the evidence, why it matters in plain language, and an effort estimate to fix it. A 90-day plan puts the fixes in order. A one-page summary is written for your board, with no jargon.
The report is yours. Your team can fix everything in it without us, and the plan is written so they can.
Want this for your team? Book this workshop
Review report
The review report: architecture summary, findings ranked critical to low with evidence, effort to fix per finding, a 90-day plan, and a one-page summary for the board. Delivered at the closing session.
What do we need from you beforehand?
Read-only access to your repositories, your hosting console and your configuration, one account per person. If you have an architecture description, send it, even an old one. We also need a list of the systems yours connects to, and an hour or two of interviews with whoever runs it day to day. If you want an NDA, we sign one at booking.
At the closing session we need whoever decides, whoever runs your systems, whoever owns the code day to day, and whoever holds the budget for fixes. One person may cover several. Up to eight people can join.
Up to 8 at the closing session
- Whoever runs the system today
- The person who would fund the fixes
Where does the work live afterward?
Everything happens in your UnflowHub™ workspace: the access checklist, the agreed scan plan, the findings, the report and the 90-day plan. Every finding is a record with an owner, a status and a due date, so your team can work through the plan and mark fixes as done. You keep access afterward, whoever does the fixing.
See how UnflowHub™ works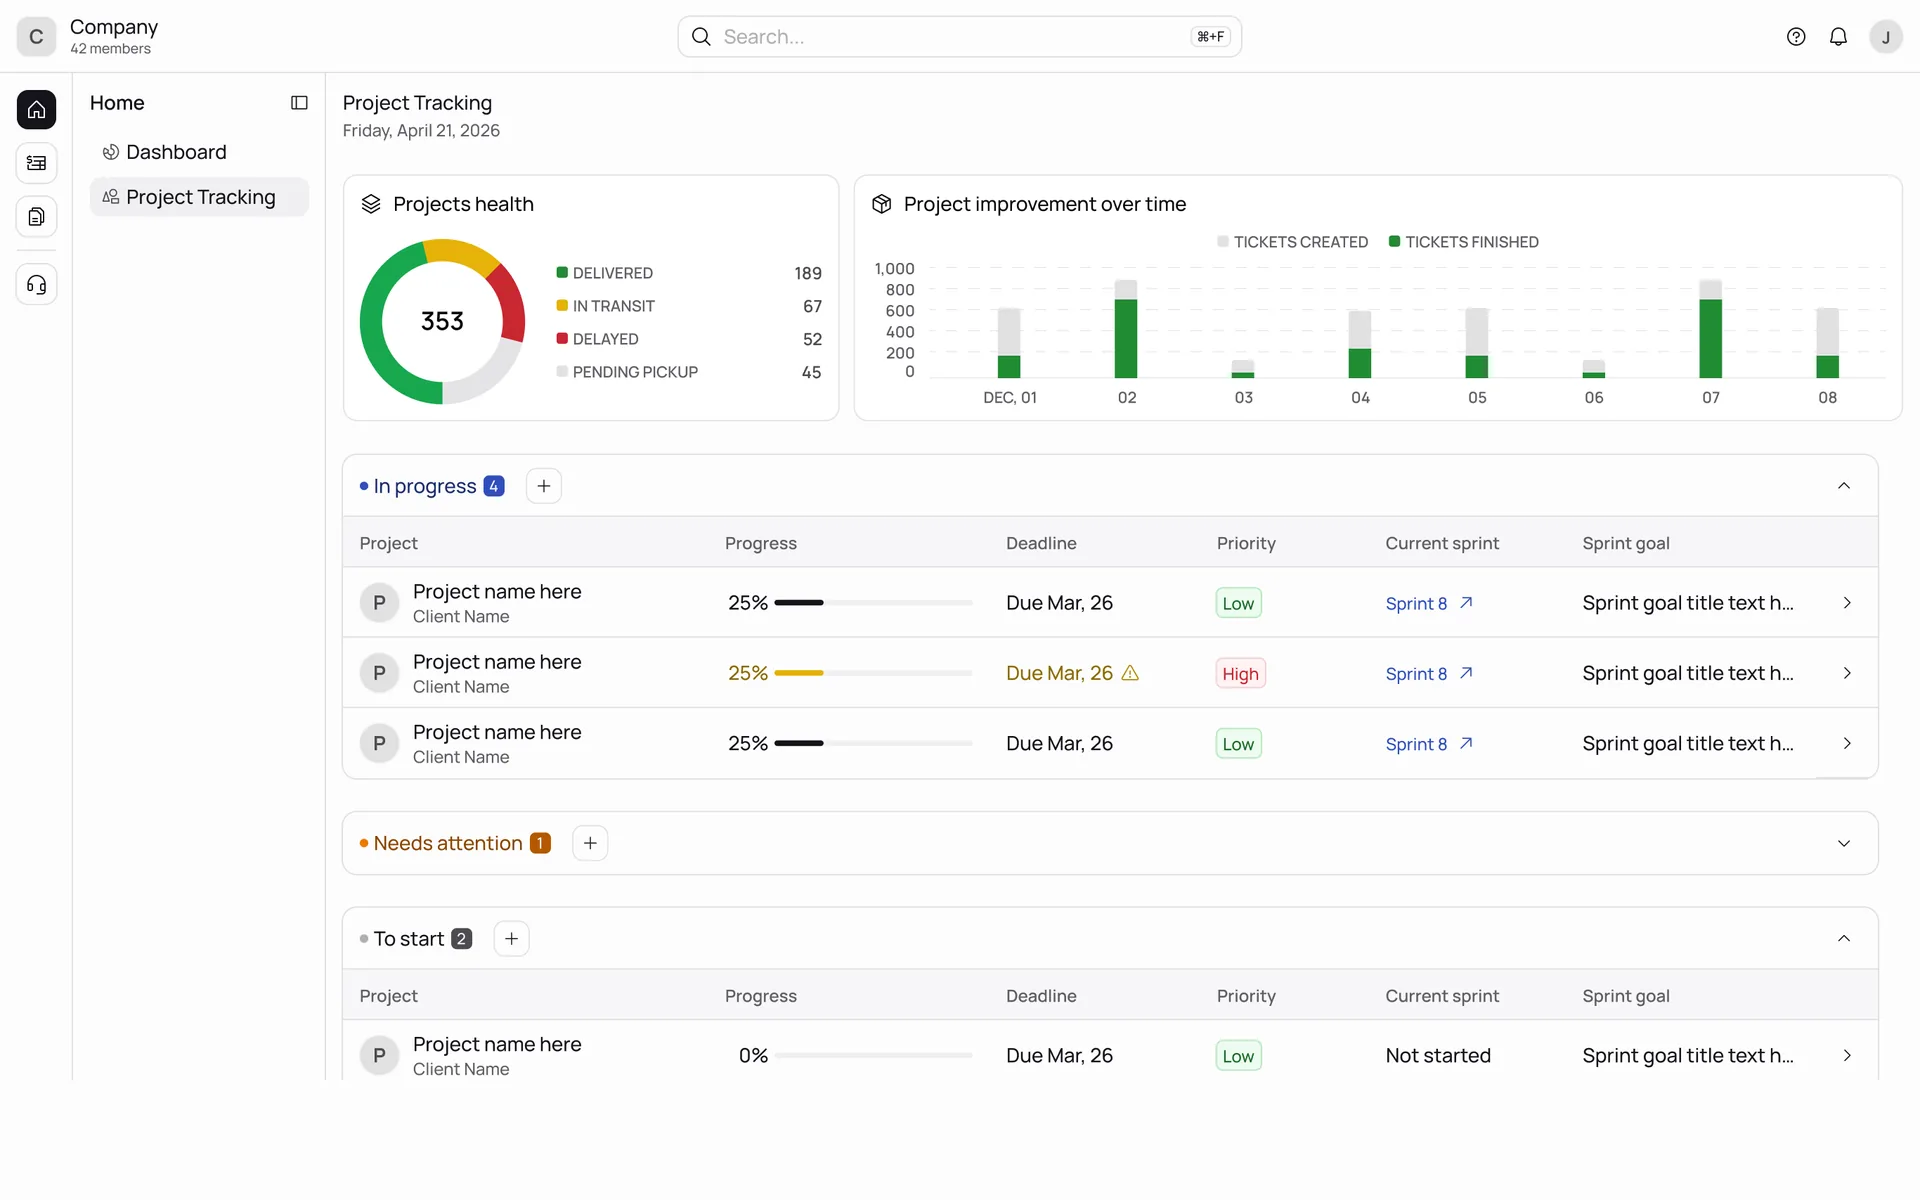
What’s the investment? How is it paid?
$12,450
$9,960
Per cohort, not per seat. Up to 8 at the closing session
$12,450 with the year-end offer, per cohort, up to 8 at the closing session
- Applies to One workshop, booked by December 15 and delivered by March 31
- BundlesWhichever is better. We never go past 25% off
- To book 50% on booking, 50% when we deliver the written output
- Credit The full fee comes off the first three months of a maintenance retainer that starts within 30 days of the workshop, up to the price of those three months
- Travel On-site anywhere in the US, in Portugal, and in Europe as far as the Netherlands. Travel is free within 50 miles of Dallas or Austin and 31 miles of Porto. Farther away, it is a fixed fee by distance, shown before you book.
Paid, and the date is held. A confirmation is on its way by email.
Payment was not completed, so nothing has been charged. Your request still reached us. Pick the slot again below, or we will send an invoice.
Your bank has not answered yet. Nothing has been charged and the date is not held until it clears, usually within a few minutes. We will email you either way.
Book it
Pick a slot, and pay the first half.
$6,225 now, $6,225 when we deliver the written output. If none of these times suit, say so and we offer two or three dates within four weeks.
Stripe handles the card, so we never see the number. The date is held once the deposit clears.
Year-end offer: for a session on or before March 31, both halves are 20% less. Checkout shows the offer price.
- Day
- Time
- Details
What happens after?
It depends on what we find.
Questions people ask.
Do you need write access to our systems?
No. Read-only access only, one account per person, with the least privilege the review needs. All of it is removed the day we finish, and we confirm that in writing.
Will you change anything in production?
No. We make no changes during a review. Every automated scan is agreed with you in writing beforehand: what runs, against what, and when.
What if you find something serious halfway through?
We tell whoever runs your systems the same day, with what we found and what to do first. If it is a password or key, we never copy it. We tell you where it is so you can change it.
Is this a penetration test?
No. A penetration test attacks a running system from the outside. We read the code, the configuration and the hosting setup from the inside, and talk to the people who run it. Many issues a pen test would find, we find first, along with the ones a pen test cannot see.
Are you certified?
Not yet. SOC 2 and ISO 27001 are both in progress, and we don’t claim a certification we don’t hold. The review follows OWASP practice, and every finding shows its evidence so your team can check it.
Who does the review?
A senior engineer who builds and runs production systems for clients, with a lead facilitator who runs the interviews and presents the findings. A second engineer checks the report before you see it.
Do we have to hire you to fix things?
No. The report and the 90-day plan are written so your team, or anyone else, can do the work. Some clients fix everything themselves.
Remote or on-site?
The review is remote. The closing session can be remote or on-site. On-site travel is free near our bases in Dallas, Austin and Porto, and a fixed fee farther away, shown before you book.
What does it look like if our system is a mess?
The report says so, in plain words, and still gives you an order of fixes. Sometimes the right answer is a rebuild. If it is, we say that too, and explain why.
Can you sign an NDA?
Yes. We offer one at booking, before you share any access or documents.
Find out what is under the hood.
Two weeks with the engineers who would do the work, and a ranked report you keep.